Posts tagged: Secure by Design
This tag lists the series newest-first. For the full roadmap — 36 posts across 12 series, in reading order, mapped to OWASP and CySA+ — see the Secure by Design front page.
← View all posts
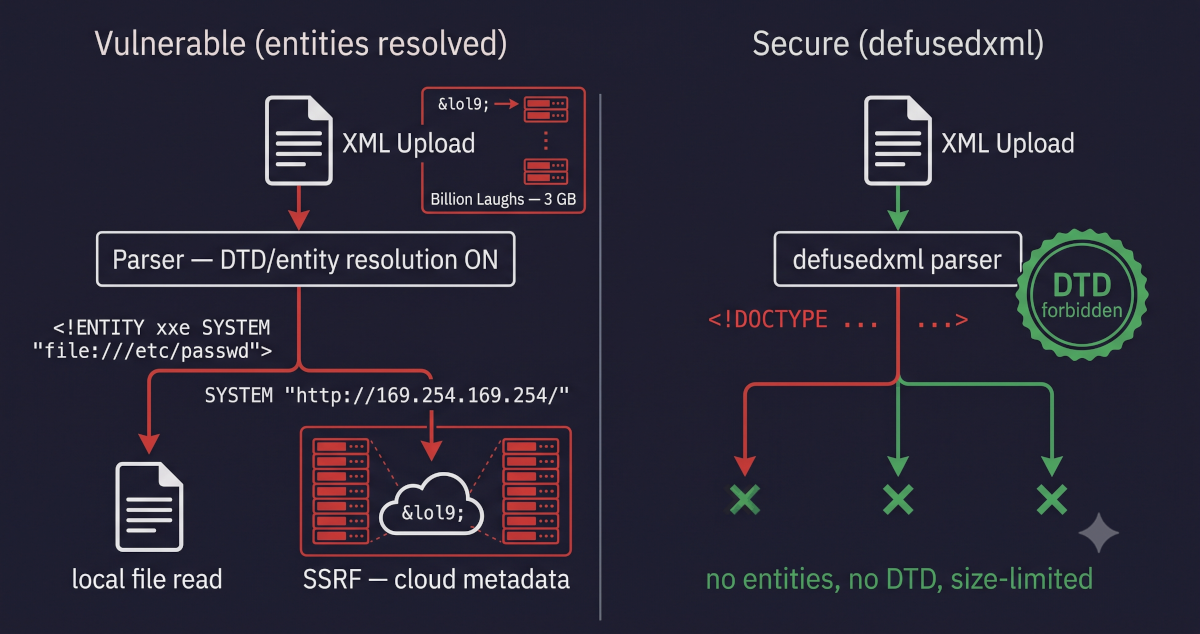
XXE in Django: how external entities read files and reach the metadata endpoint, Billion Laughs exhausts memory, and defusedxml is the fix. OWASP A02.
Read more →
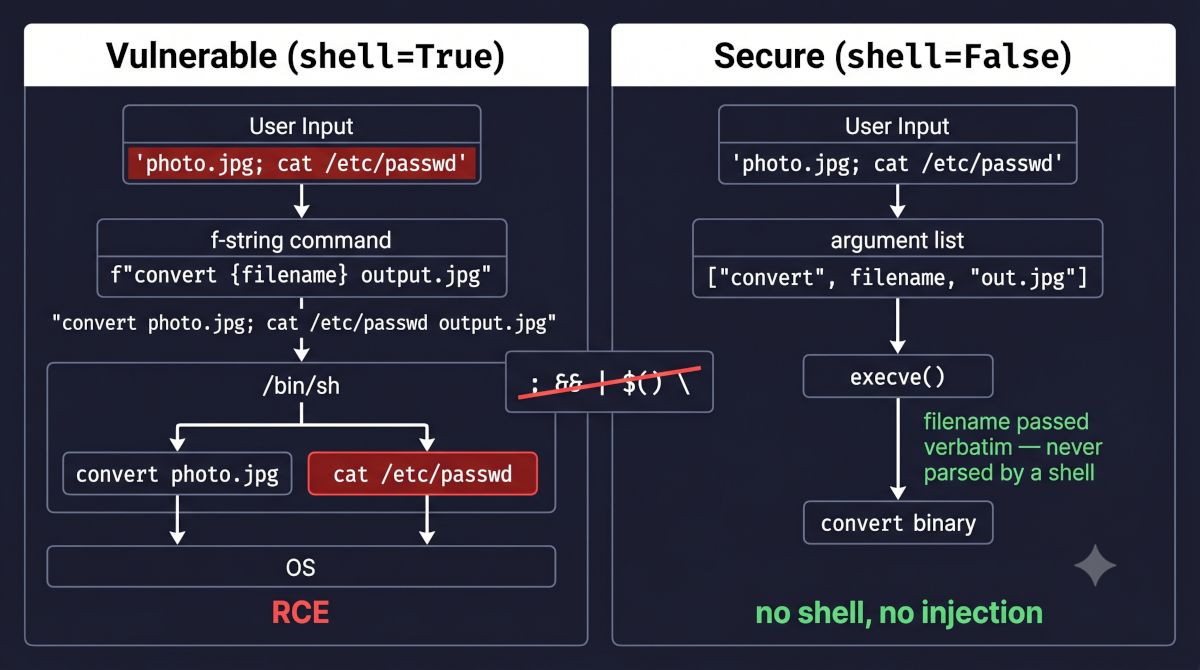
OS Command Injection in Django: how shell=True turns user input into RCE, why shell=False with an argument list stops it. OWASP A05, CVE-2016-3714.
Read more →
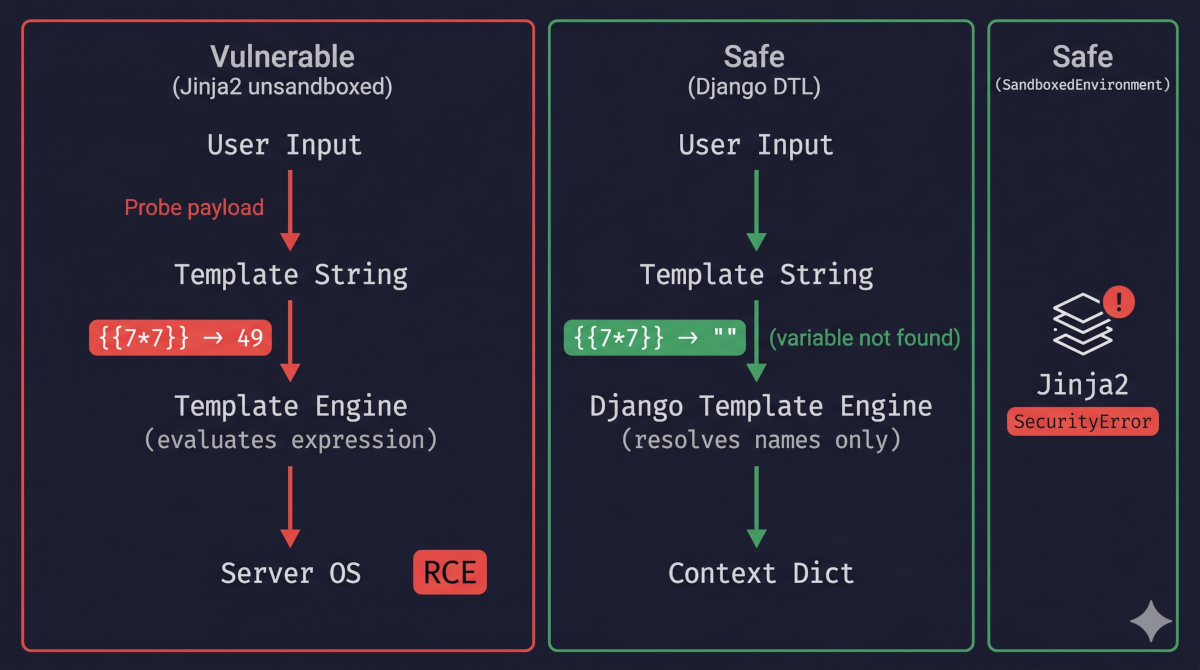
SSTI in Django: how Jinja2 MRO traversal achieves RCE, why Django's DTL is safe by design, and where that guarantee evaporates. OWASP A05, CVE-2022-22954.
Read more →
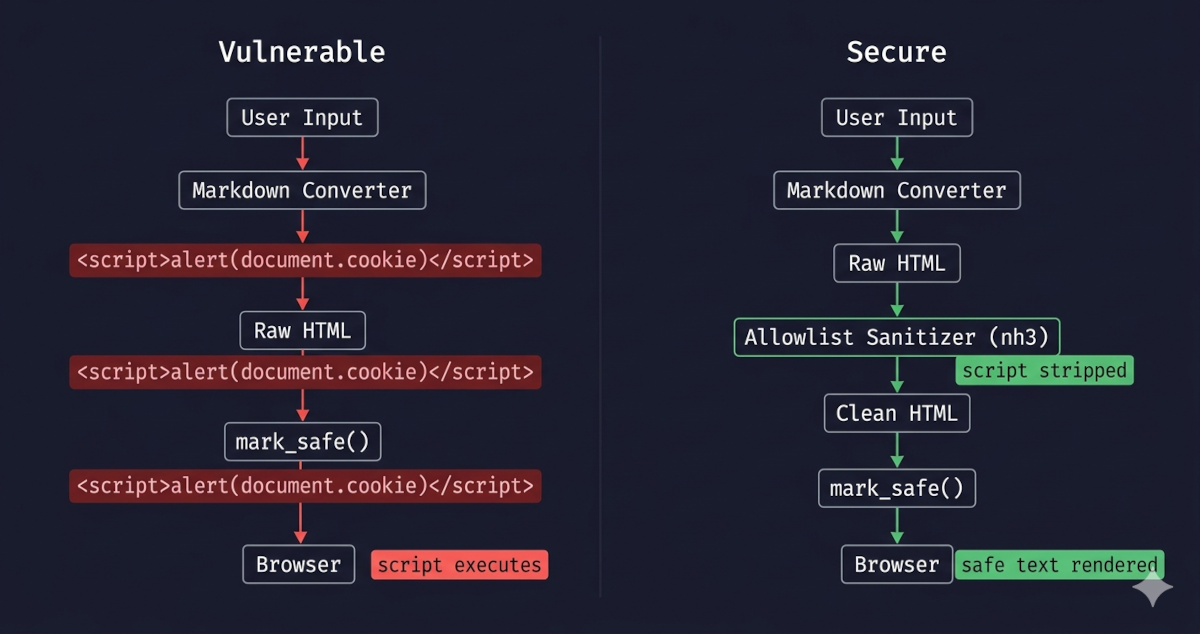
XSS in Django: how stored, reflected and DOM-based attacks work, why mark_safe() and unsafe Markdown open the same hole, and how to migrate to nh3.
Read more →
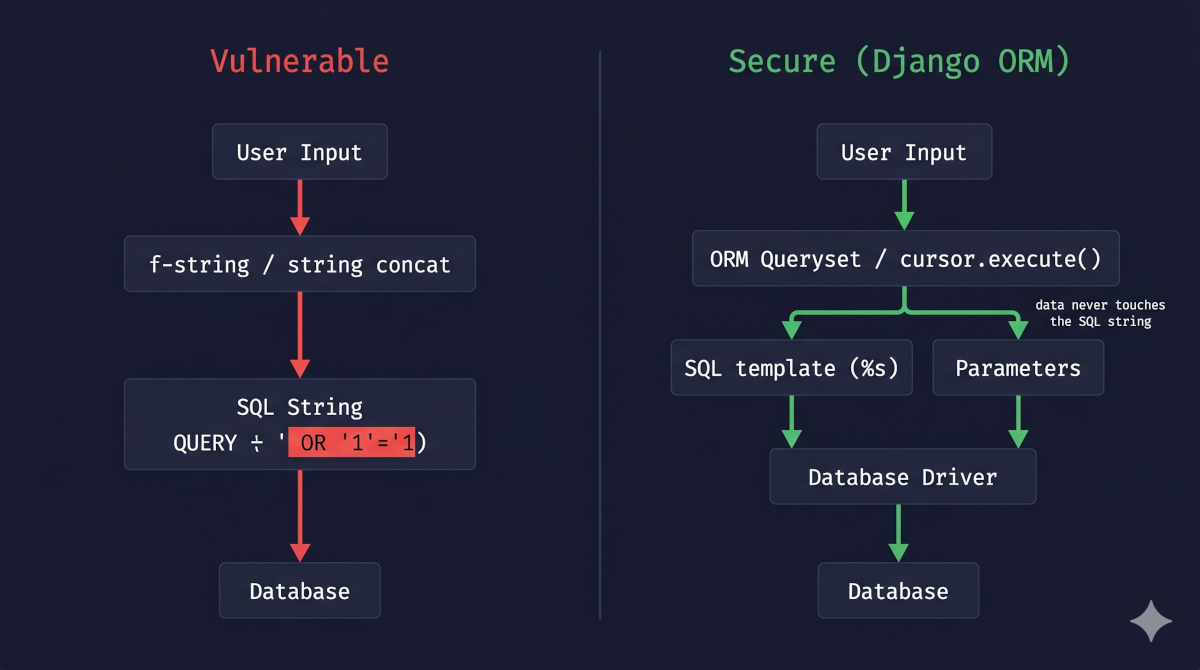
SQL Injection: how attackers exploit unsanitised queries, why Django's ORM stops them, and where the protection ends. OWASP A05, CySA+ VM.
Read more →