Posts tagged: Secure by Design
This tag lists the series newest-first. For the full roadmap — 36 posts across 12 series, in reading order, mapped to OWASP and CySA+ — see the Secure by Design front page.
← View all posts
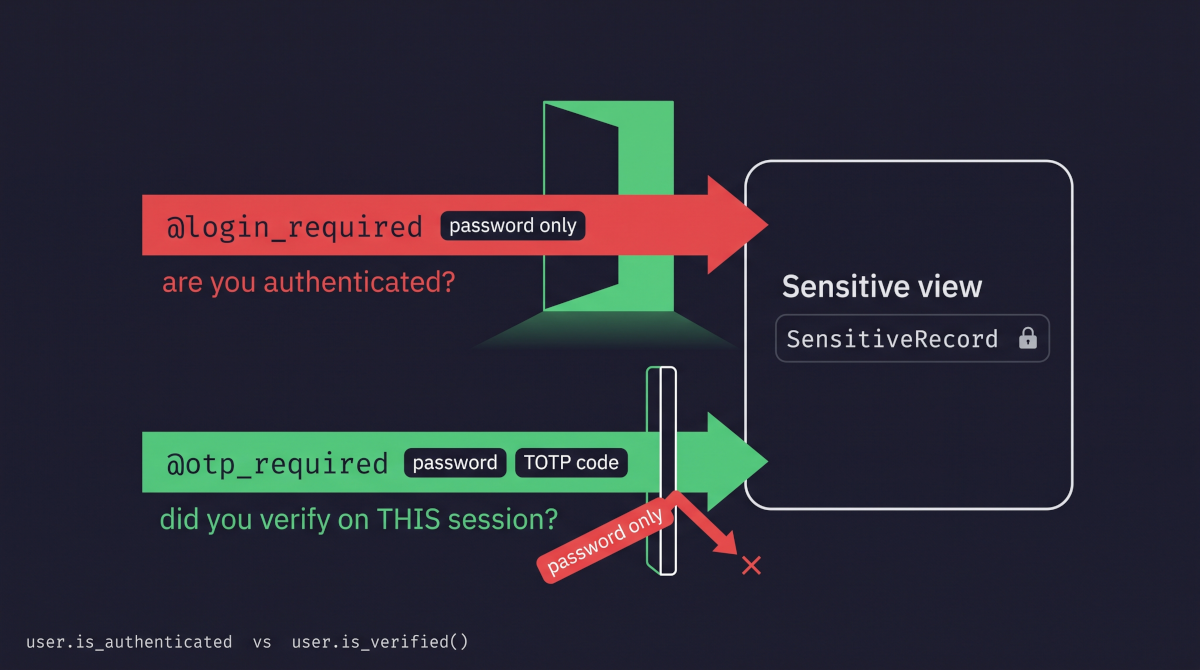
MFA in Django: why @login_required cannot see a second factor, how one path that skips it undoes the whole rollout, and what otp_required fixes. OWASP A07.
Read more →
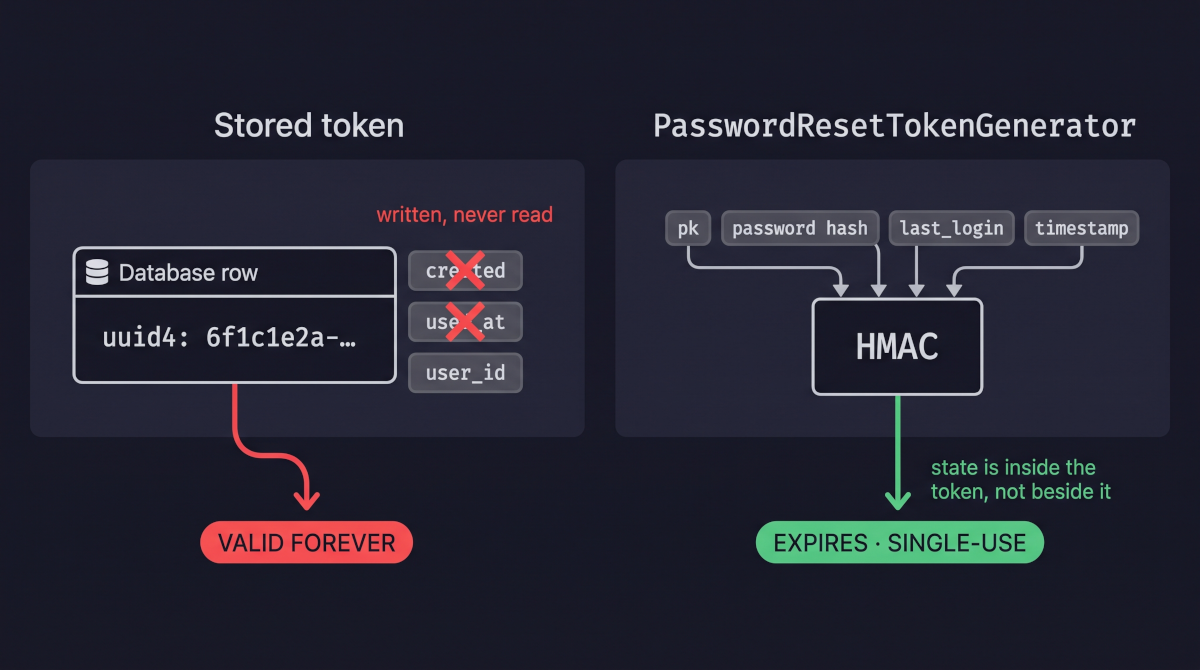
Django password reset flaws: tokens that never expire or retire, host-header link poisoning, and the one call that fixes three of them. OWASP A07.
Read more →
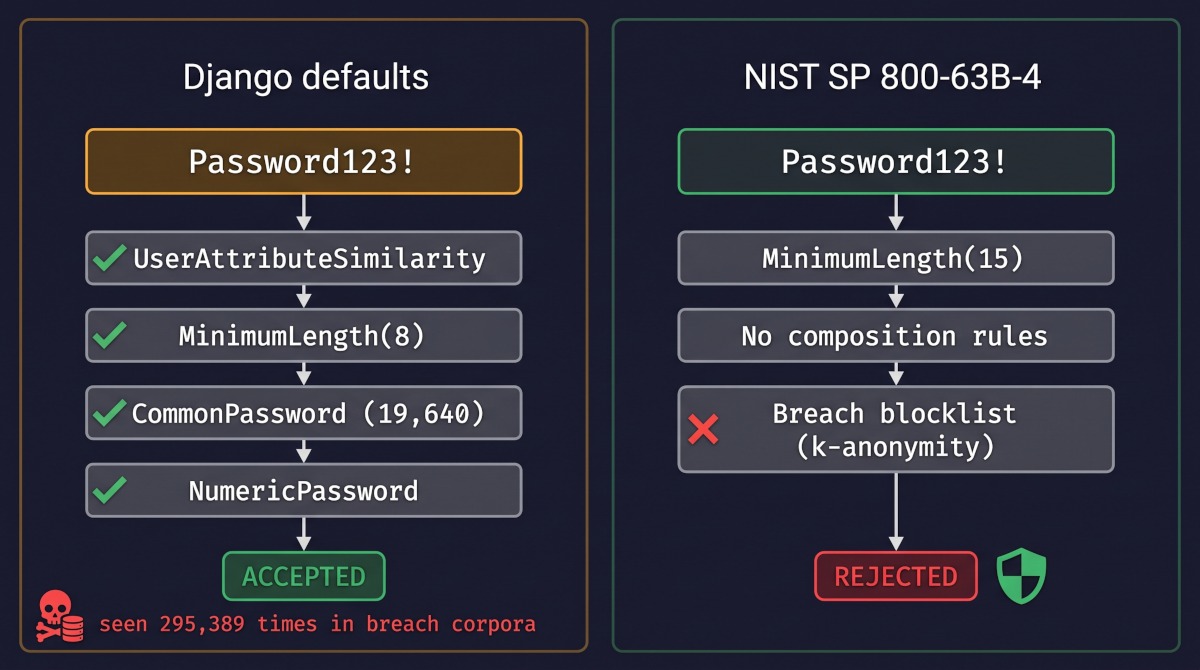
Weak passwords in Django: why the four default validators accept Password123!, what NIST 800-63B-4 now forbids, and how to check a breach list. OWASP A07.
Read more →
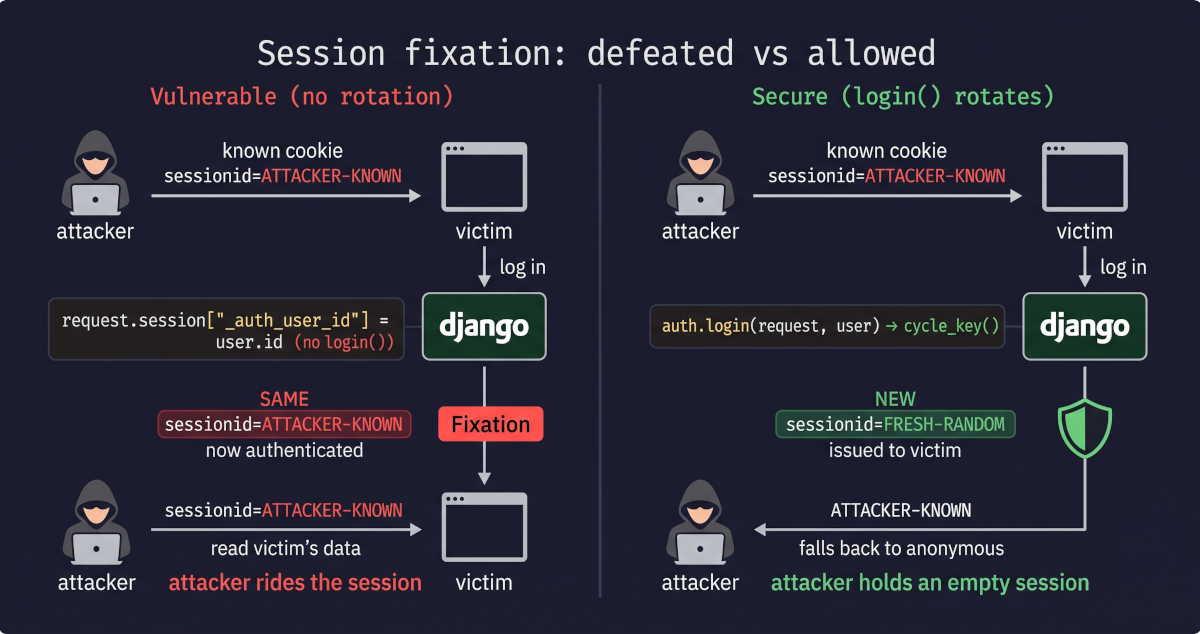
Session hijacking and fixation in Django: why login() rotates the session key, a hand-rolled flow undoes it, plus cookie flags. OWASP A07.
Read more →
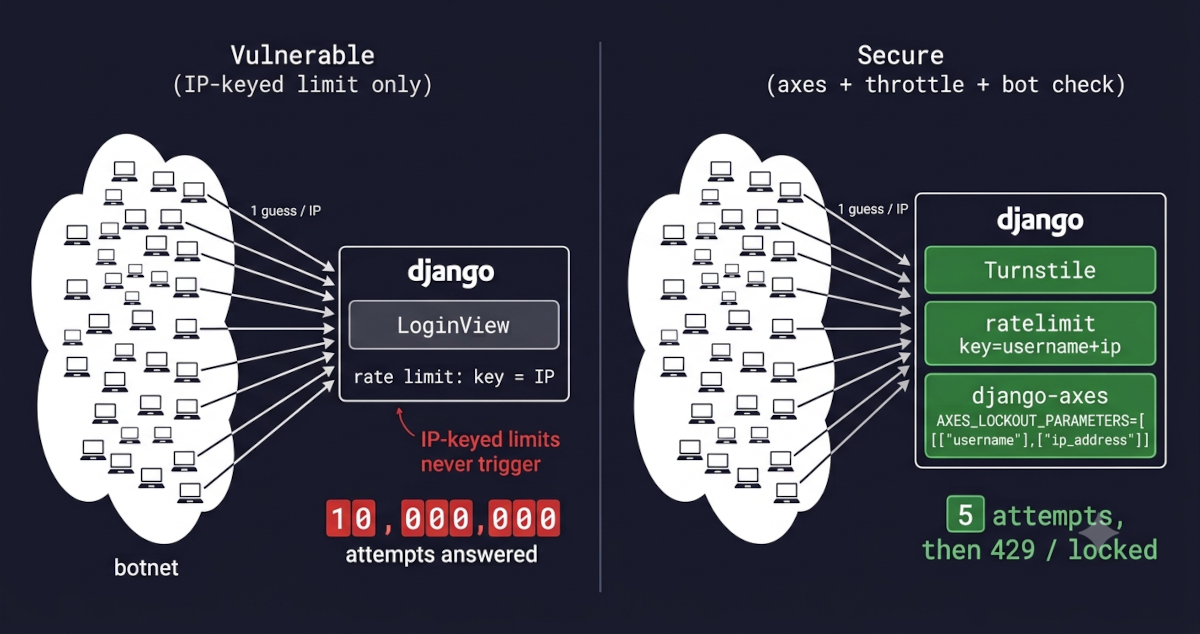
Brute force in Django: why auth never throttles logins, how django-axes and rate limiting close the gap, and why IP-keyed limits fail. OWASP A07.
Read more →
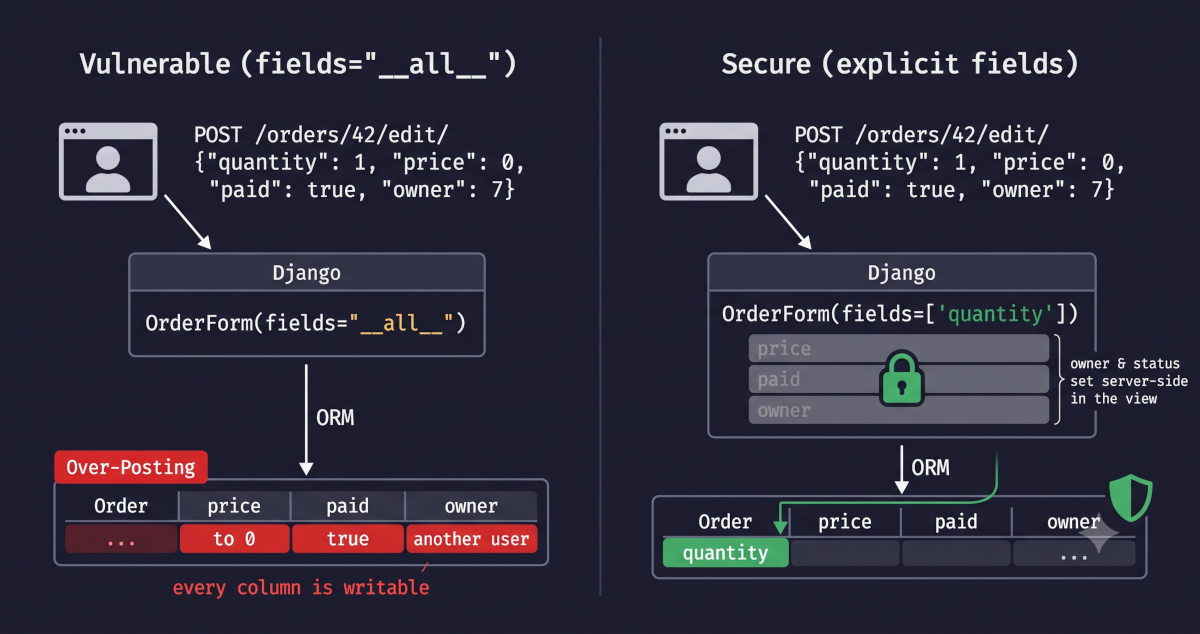
Mass assignment in Django: how fields='__all__' lets attackers over-post fields like status or owner, and how explicit field lists stop it. OWASP A08.
Read more →
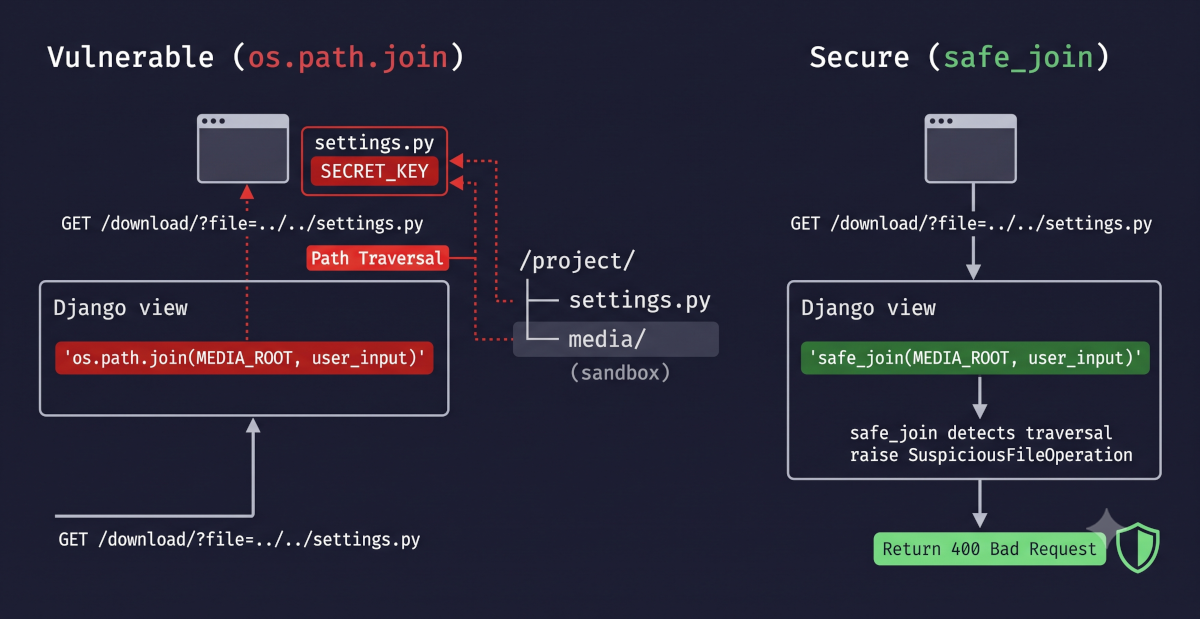
Path traversal in Django: how os.path.join lets attackers escape MEDIA_ROOT, why safe_join stops it, and when FileField eliminates the risk. OWASP A01.
Read more →
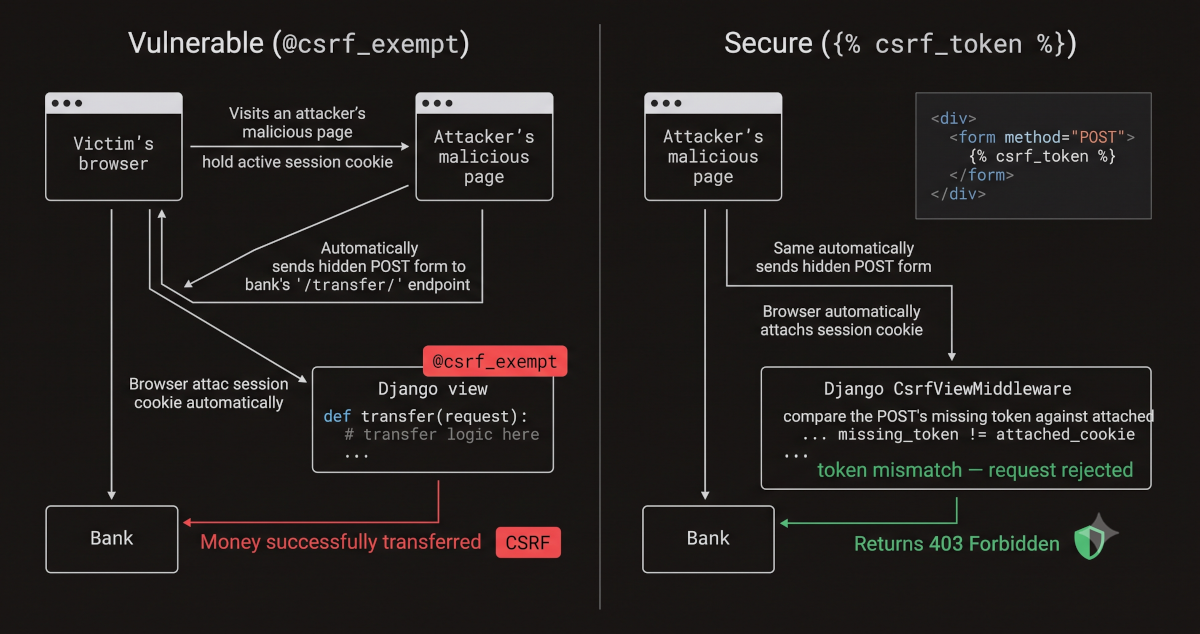
CSRF in Django: how hidden forms ride the victim's session cookie, why @csrf_exempt is dangerous, and how CsrfViewMiddleware stops it. OWASP A01.
Read more →
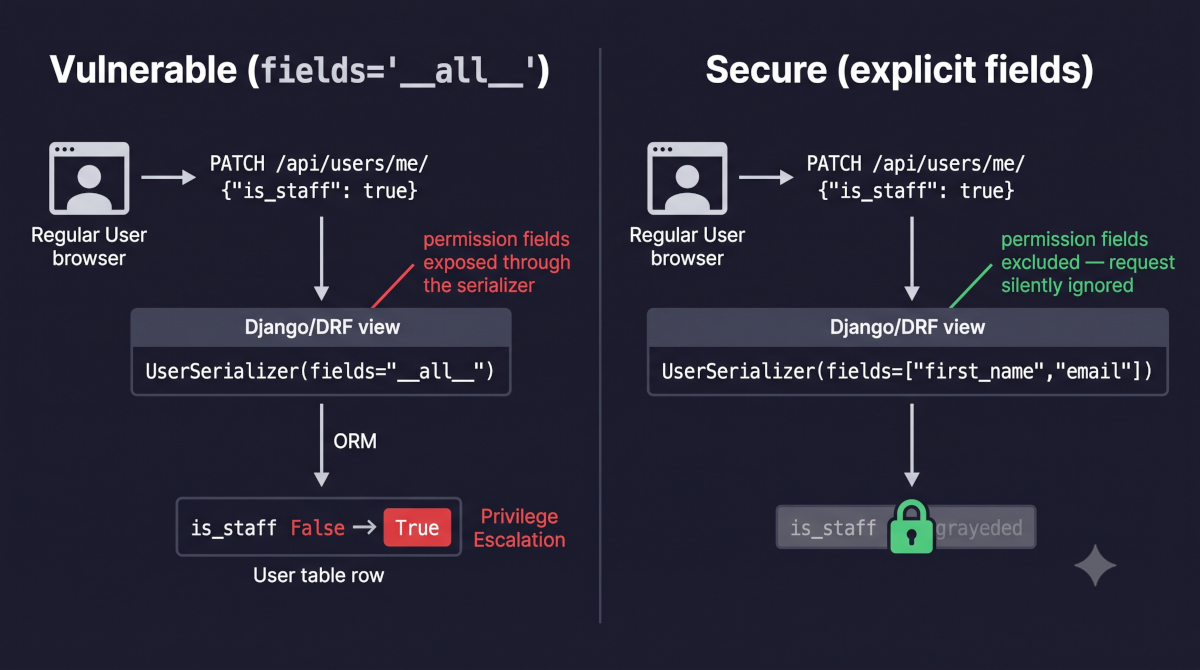
Privilege escalation in Django: how fields='__all__' exposes is_staff and is_superuser, and how explicit field lists stop it. OWASP A01.
Read more →
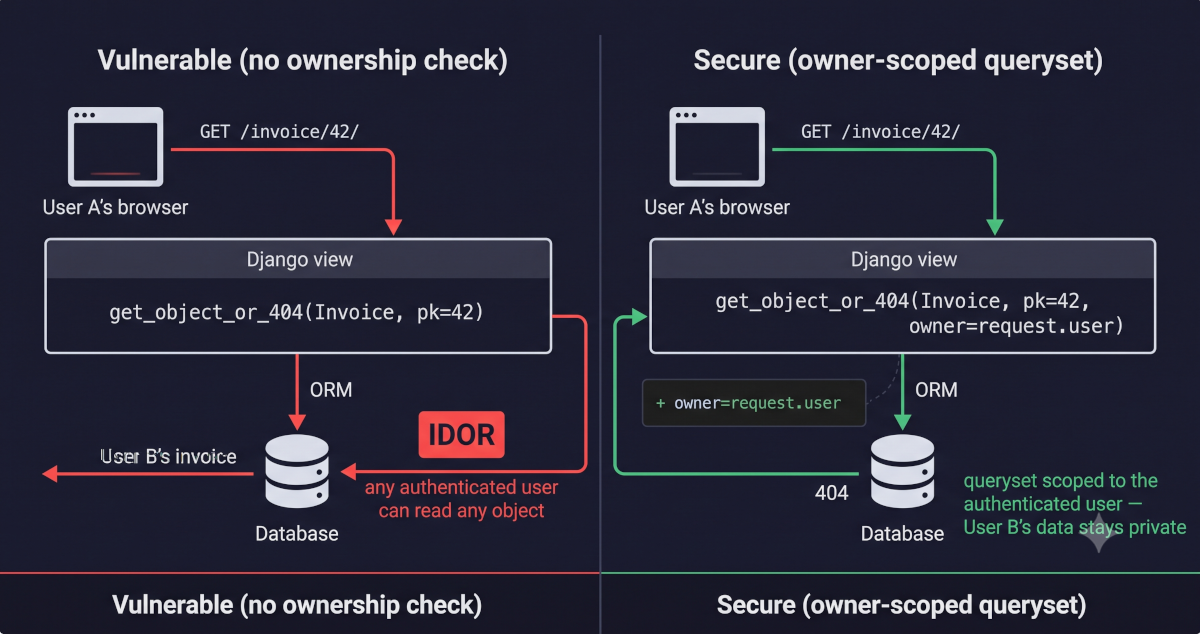
IDOR in Django: how swapping a URL ID leaks another user's data, why login_required is not authorization, and how to scope querysets. OWASP A01.
Read more →